Web application security scanners can help find weaknesses in websites, but this roundup’s ten entries are books about web security and penetration testing—not standalone scanning software. I’d put Grokking Web Application Security first for its accessible path into the subject, with Hands-on Penetration Testing for Web Applications and Automated Penetration Testing standing out for practical testing and emerging automation. The main tradeoff is whether you want approachable foundations, hands-on tool workflows, or advanced techniques that assume more experience. A book can teach scanning concepts, but it cannot replace a scanner or verify findings against your live application. Continue reading for a comparison of what each title can teach, who it suits, and where its limits lie.

Get business pricing on monitors, keyboards and dev gear
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
Key Takeaways
- This list contains learning resources, not scanner products. Buyers seeking software for automated or interactive scanning will need to compare actual scanner platforms separately.
- Grokking Web Application Security is the clearest beginner-oriented starting point among the titles, while advanced tool-focused books make more sense after learning web fundamentals.
- Hands-on Penetration Testing for Web Applications points readers toward practical testing workflows; it is a closer fit for applied learning than a broad introductory guide.
- Automated Penetration Testing focuses on AI agents, making it the most specialized choice here rather than a general-purpose first book.
- The Web Application Hacker’s Handbook appears twice under different subtitles. Check the exact edition and contents before buying to avoid assuming the two listings offer different coverage.
| Beginner’s Guide to Web Application Penetration Testing |  | Best for Beginners | Product type: Introductory guide | Subject: Web application penetration testing | Intended audience: Beginners | VIEW LATEST PRICE | See Our Full Breakdown |
| Web Application Security: Exploitation and Countermeasures for Modern Web Applications |  | Best for Understanding Findings and Fixes | Product type: Book | Subject: Web application security | Coverage: Exploitation and countermeasures | VIEW LATEST PRICE | See Our Full Breakdown |
| The Web Application Hacker’s Handbook: Discovering and Exploiting Security Flaws |  | Best Methodology Reference | Product type: Book | Subject: Web application security testing | Coverage: Discovering and exploiting security flaws | VIEW LATEST PRICE | See Our Full Breakdown |
| Hands-on Penetration Testing for Web Applications: Web Security Testing on Modern Applications – 2nd Edition |  | Best for Practical Testing | Product type: Book | Edition: 2nd Edition | Subject: Web application penetration testing | VIEW LATEST PRICE | See Our Full Breakdown |
| The Web Application Hacker’s Handbook: Finding and Exploiting Security Flaws | 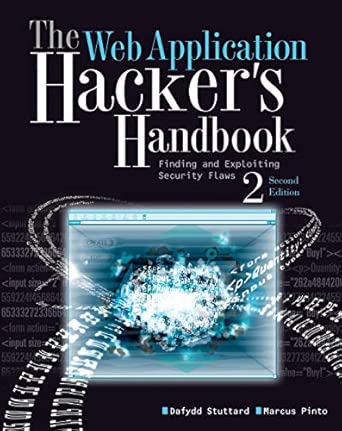 | Best for Focused Flaw-Finding Study | Product type: Book | Subject: Web application security | Coverage: Finding and exploiting security flaws | VIEW LATEST PRICE | See Our Full Breakdown |
| Automated Penetration Testing: Building Autonomous AI Agents for Web Security |  | Best for AI-Driven Testing Research | Product type: Book | Subject: Automated penetration testing | Focus: Building autonomous AI agents | VIEW LATEST PRICE | See Our Full Breakdown |
| Web Application Security 101: A Comprehensive Guide to Penetration Testing |  | Best for a General Introduction | Product type: Book | Subject: Web application security | Secondary subject: Penetration testing | VIEW LATEST PRICE | See Our Full Breakdown |
| Ultimate Pentesting for Web Applications: Advanced Web App Security with Burp Suite, ZAP Proxy, Fiddler, Charles, and Python |  | Best for Comparing Testing Tools | Product type: Book | Format: English Edition | Named tools: Burp Suite, ZAP Proxy, Fiddler, Charles | VIEW LATEST PRICE | See Our Full Breakdown |
| Web Application Security: Finding and Fixing Exploits in Modern Websites |  | Best for Developer Remediation | Product type: Book | Subject: Web application security | Primary audience: Developers | VIEW LATEST PRICE | See Our Full Breakdown |
| Grokking Web Application Security |  | Best for a Broad Security Primer | Product type: Book | Subject: Web application security | Named scanners: Not specified | VIEW LATEST PRICE | See Our Full Breakdown |
| web application security scanner | Product type | Subject | Coverage |
|---|---|---|---|
| Beginner’s Guide to Web Applic | Introductory guide | Web application penetration testing | Fundamentals, essential concepts, and tools |
| Web Application Security: Expl | Book | Web application security | Exploitation and countermeasures |
| The Web Application Hacker’s H | Book | Web application security testing | Discovering and exploiting security flaws |
| Hands-on Penetration Testing f | Book | Web application penetration testing | Vulnerability assessment and exploitation |
| The Web Application Hacker’s H | Book | Web application security | Finding and exploiting security flaws |
| Automated Penetration Testing: | Book | Automated penetration testing | — |
| Web Application Security 101: | Book | Web application security | — |
| Ultimate Pentesting for Web Ap | Book | Web application penetration testing | — |
| Web Application Security: Find | Book | Web application security | Identifying and understanding vulnerabilities |
| Grokking Web Application Secur | Book | Web application security | — |
More Details on Our Top Picks
Beginner’s Guide to Web Application Penetration Testing
This is the most approachable entry point in this group for readers who need to learn how web application testing works before choosing or interpreting a scanner. Its beginner-friendly explanations, practical examples, and hands-on exercises can help readers connect common testing concepts to the findings automated tools report. Compared with The Web Application Hacker’s Handbook: Discovering and Exploiting Security Flaws, it is positioned for a gentler start rather than broad, technically demanding coverage. That accessibility is also the tradeoff: practitioners already familiar with web security may find its treatment too introductory, and the supplied details do not identify specific scanners, protocols, or testing frameworks. It is a learning resource, not a scanning product, so buyers seeking software to scan an application should choose an actual security tool instead.
Pros:- Beginner-friendly explanations lower the barrier to learning web application testing.
- Practical examples connect concepts to applied testing work.
- Hands-on exercises give learners a way to practice rather than only read.
- A useful foundation for understanding scanner output and manual follow-up.
Cons:- Limited depth may leave experienced practitioners wanting more advanced material.
- Provided details do not name specific scanners, technologies, or testing frameworks.
- It teaches testing rather than scanning applications automatically.
Best for: New cybersecurity learners who want a guided introduction to web application penetration testing and the concepts behind scanner findings.
Not ideal for: Security teams seeking a deployable scanner, or experienced testers who need advanced technical depth and explicitly documented tool coverage.
- Product type:Introductory guide
- Subject:Web application penetration testing
- Intended audience:Beginners
- Coverage:Fundamentals, essential concepts, and tools
- Learning approach:Step-by-step methodologies
- Practice material:Practical examples and hands-on exercises
Our verdict“Choose this as a first learning resource if you want clear explanations and exercises, not a scanner or an advanced reference.”
Web Application Security: Exploitation and Countermeasures for Modern Web Applications
This book earns a distinct place for readers who want to connect how vulnerabilities are exploited with the countermeasures used to address them. That perspective is useful when a scanner flags a weakness: a team needs to understand both the risk behind the finding and the kind of response it calls for. Compared with the beginner-oriented Beginner’s Guide to Web Application Penetration Testing, this title is framed around exploitation and defense rather than a broad introductory learning path. The supplied product information is sparse, however: it does not specify particular vulnerabilities, scanner integrations, tools, or a level of technical difficulty. I would treat it as a security reference, not a ready-made scanning solution, and readers who need step-by-step exercises may prefer the more explicitly hands-on Hands-on Penetration Testing for Web Applications.
Pros:- Pairs vulnerability exploitation with defensive countermeasures.
- Focuses on modern web applications, according to the product description.
- Can help readers reason about the security implications behind scanner findings.
Cons:- Provided details do not identify specific vulnerabilities, tools, or scanner coverage.
- No hands-on exercises or step-by-step structure are confirmed in the supplied description.
- The intended skill level is not specified.
Best for: Developers and security learners who want to study the relationship between web application exploits and defensive countermeasures.
Not ideal for: Buyers looking for an automated scanner, a clearly documented beginner curriculum, or confirmed tool-specific procedures.
- Product type:Book
- Subject:Web application security
- Coverage:Exploitation and countermeasures
- Application focus:Modern web applications
- Scanner software:Not identified in the supplied product details
- ASIN:1098143930
Our verdict“Pick this for an exploitation-and-defense perspective, while choosing a hands-on guide if practical exercises are your priority.”
The Web Application Hacker’s Handbook: Discovering and Exploiting Security Flaws
This is the strongest fit in the lineup for readers seeking systematic web application security testing rather than a short introduction. Its stated coverage combines flaw discovery, exploitation, practical examples, tool recommendations, and step-by-step methodology, giving testers a framework for investigating issues beyond a scanner’s initial alert. Compared with Beginner’s Guide to Web Application Penetration Testing, it offers broader, more technical coverage, but that breadth can make it a harder first read for someone new to security. The description presents the techniques as comprehensive, yet it does not name particular scanner products or establish how current every technique is for a buyer’s environment. This is a reference for learning and manual testing; it does not replace the automated scanning software itself.
Pros:- Covers a broad range of web security flaws and testing techniques.
- Step-by-step methodology supports more systematic manual assessment.
- Practical examples and real-world tool recommendations connect concepts to testing.
- Useful for understanding how to investigate findings beyond automated detection.
Cons:- Dense technical content may challenge readers new to web security.
- The supplied details do not name specific scanners or confirm compatibility with current tools.
- A handbook cannot perform automated scans on an application.
Best for: Penetration testers and security learners who want a structured reference for discovering, validating, and understanding web application flaws.
Not ideal for: Absolute beginners who need a gentle first introduction, or teams seeking a scanner they can deploy rather than a testing guide.
- Product type:Book
- Subject:Web application security testing
- Coverage:Discovering and exploiting security flaws
- Methodology:Step-by-step testing guidance
- Examples:Practical examples
- Tools:Tool recommendations and real-world tool examples
- Intended audience:Beginners and experienced penetration testers; content may challenge absolute beginners
Our verdict“Choose this as a substantial methodology reference if you already have some technical grounding and want to go beyond scanner alerts.”
Hands-on Penetration Testing for Web Applications: Web Security Testing on Modern Applications – 2nd Edition
The second edition is the clearest choice here for readers who learn by working through practical web application testing. Its hands-on approach and stated updates for contemporary web technologies make it a better match for testers who want applied guidance than Web Application Security: Exploitation and Countermeasures for Modern Web Applications, whose supplied description does not confirm exercises or a practical workflow. This book focuses on vulnerability assessment and exploitation, so it can help readers build testing skills relevant to interpreting scanner results and following up manually. The tradeoff is that it assumes basic knowledge of web technologies and prioritizes practice over theoretical foundations. The product details also do not name particular scanners or confirm that the book teaches how to configure any one scanning platform.
Pros:- Hands-on approach emphasizes applied testing rather than concepts alone.
- Covers vulnerability assessment and exploitation.
- Second edition is described as updated for contemporary web technologies.
- Practical testing methods can complement automated scanner findings.
Cons:- Assumes a basic understanding of web technologies.
- Places less emphasis on theoretical foundations.
- The supplied details do not identify specific scanners or tool integrations.
Best for: Learners with basic web technology knowledge who want applied guidance on assessing and exploiting vulnerabilities in modern applications.
Not ideal for: Complete beginners seeking foundational explanations, or buyers who need a scanner-specific setup manual or a theory-first security text.
- Product type:Book
- Edition:2nd Edition
- Subject:Web application penetration testing
- Application focus:Modern web applications
- Coverage:Vulnerability assessment and exploitation
- Learning approach:Hands-on practical guidance
- Prerequisite:Basic understanding of web technologies
Our verdict“Choose this for practical testing guidance if you already understand web basics and want more applied work than a general security overview provides.”
The Web Application Hacker’s Handbook: Finding and Exploiting Security Flaws
This handbook is aimed at readers who want to study finding and exploiting web application flaws, a useful manual-testing complement to automated scanner results. Its stated subject overlaps with The Web Application Hacker’s Handbook: Discovering and Exploiting Security Flaws, so the supplied descriptions do not establish a meaningful technical advantage for one title over the other. This edition’s product information is especially limited: no tool recommendations, methodology details, examples, or audience level are provided. That makes it a less evidence-backed pick than the handbook with documented practical examples and systematic guidance, and buyers should not assume the two listings differ in coverage based on their titles alone. It is a book, not scanning software, and the available details do not confirm scanner-specific instruction.
Pros:- Directly addresses finding and exploiting web application flaws.
- Handbook format suggests a reference-oriented role for security study.
- Subject matter can support manual investigation of scanner alerts.
Cons:- Supplied product details do not describe methodology, examples, or tools.
- Its distinction from the other listed Web Application Hacker’s Handbook is unclear from the available information.
- No scanner functionality or scanner-specific guidance is confirmed.
Best for: Readers specifically seeking a handbook on finding and exploiting web application security flaws who can verify that this edition’s contents suit their needs.
Not ideal for: Buyers who need confirmed exercises, tool recommendations, a defined learning level, or an automated web application scanner.
- Product type:Book
- Subject:Web application security
- Coverage:Finding and exploiting security flaws
- Format description:Handbook
- Tools:Not specified in the supplied product details
- Methodology:Not specified in the supplied product details
- ASIN:1118026470
Our verdict“Consider this only if its specific edition and contents meet your needs; the other handbook listing has clearer documented testing detail.”
Automated Penetration Testing: Building Autonomous AI Agents for Web Security
This title has the most specialized angle in the group: building autonomous AI agents for web security rather than learning a broad set of manual testing workflows. That focus may suit security engineers exploring how automation could assist penetration testing, while Ultimate Pentesting for Web Applications is more clearly oriented around named tools such as Burp Suite and ZAP Proxy. The title alone does not establish which techniques, platforms, or safeguards the book covers, so I would treat it as a focused study rather than a proven scanner manual. Its main tradeoff is that readers seeking immediately usable scanner instructions may find the subject narrower or more conceptual than the practical remediation focus of Web Application Security: Finding and Fixing Exploits in Modern Websites.
Pros:- Centers on autonomous AI agents for web security
- Connects automation concepts to penetration testing
- Offers a distinct subject focus compared with tool-oriented guides
Cons:- Available information does not identify specific scanners, platforms, or techniques
- The AI-agent focus may be too narrow for readers seeking general web application testing guidance
Best for: Security engineers and technically experienced readers researching autonomous AI agents for web penetration testing.
Not ideal for: Beginners seeking a step-by-step guide to established scanners, since the available description does not specify foundational instruction or tool coverage.
- Product type:Book
- Subject:Automated penetration testing
- Focus:Building autonomous AI agents
- Application area:Web security
- Scanner products named:Not specified
- Programming languages:Not specified
Our verdict“Choose this title if your main interest is AI-agent approaches to penetration testing, not a documented walkthrough of conventional web scanners.”
Web Application Security 101: A Comprehensive Guide to Penetration Testing
The title presents this as a broad introduction to web application security and penetration testing, making it a more general starting point than Automated Penetration Testing: Building Autonomous AI Agents for Web Security, which centers on a specialized automation topic. That breadth could help readers seeking a security overview before choosing a scanner or testing workflow. However, the available description does not name tools, exercises, or remediation methods, so I cannot treat it as a hands-on scanner tutorial. Compared with Ultimate Pentesting for Web Applications, which explicitly names Burp Suite, ZAP Proxy, Fiddler, Charles, and Python, this guide offers less confirmed detail about practical tool coverage. Its strength is the introductory scope; its uncertainty is how concretely that scope is taught.
Pros:- Addresses both web application security and penetration testing
- Has an introductory framing that may suit readers building foundational context
- Provides a broader stated scope than the AI-agent-focused title
Cons:- No specific scanners or testing tools are identified
- The available description does not confirm hands-on exercises or remediation guidance
Best for: Readers new to web application security who want a general penetration-testing guide before selecting specific scanner tools.
Not ideal for: Practitioners who need confirmed labs, named scanner instructions, or detailed remediation steps, none of which are specified in the available description.
- Product type:Book
- Subject:Web application security
- Secondary subject:Penetration testing
- Positioning:General guide
- Scanner products named:Not specified
- Format:Not specified
Our verdict“Pick this as a general entry point if you want a broad security overview and do not require confirmed tool-by-tool scanner training.”
Ultimate Pentesting for Web Applications: Advanced Web App Security with Burp Suite, ZAP Proxy, Fiddler, Charles, and Python
Among these titles, this one gives the clearest view of its toolset: it names Burp Suite, ZAP Proxy, Fiddler, and Charles, then adds Python for defensive work. That makes it a more concrete choice for readers comparing different approaches to intercepting and inspecting web traffic than Web Application Security 101, whose description does not identify any tools. The multi-tool scope may help practitioners understand alternatives rather than relying on a single scanner, but the available information does not confirm chapters, exercises, or how deeply each product is covered. Its advanced framing may also be a steeper start than Web Application Security: Finding and Fixing Exploits in Modern Websites, which is explicitly described as including remediation strategies.
Pros:- Names four web testing tools: Burp Suite, ZAP Proxy, Fiddler, and Charles
- Includes Python in a defensive-security context
- Provides a wider stated tool range than the other books in this batch
Cons:- The available description does not show how much depth each tool receives
- Advanced positioning may be less approachable for readers without security fundamentals
Best for: Practitioners who want a guide spanning several named web testing tools and Python-based defensive security.
Not ideal for: Readers looking for a clearly documented beginner curriculum or confirmed step-by-step remediation labs, since those details are not provided.
- Product type:Book
- Format:English Edition
- Named tools:Burp Suite, ZAP Proxy, Fiddler, Charles
- Programming language:Python
- Subject:Web application penetration testing
- Approach:Advanced web application security
- Python focus:Defensive security
Our verdict“Choose this if comparing several named web testing tools matters more than having a confirmed beginner path or detailed remediation outline.”
Web Application Security: Finding and Fixing Exploits in Modern Websites
This is the strongest fit here for developers who need to connect finding vulnerabilities with fixing them. Its description promises real-world exploit scenarios, practical testing techniques, and step-by-step remediation for modern applications, giving it a clearer fix-oriented path than Ultimate Pentesting for Web Applications, whose named tools are more specific than its stated remediation detail. The focus on contemporary web technologies also makes it more directly relevant to teams maintaining current sites than a general introductory guide such as Web Application Security 101. The tradeoff is that the material may be too technical for readers with no security background, and no particular scanner product is named, so buyers seeking a dedicated scanner manual should check whether its testing methods match their workflow.
Pros:- Connects vulnerability discovery with step-by-step remediation
- Describes real-world exploit scenarios and practical testing techniques
- Targets modern web technologies
- Offers a clearer developer-fix emphasis than the tool-list-focused alternative
Cons:- May be too technical for readers without prior security knowledge
- The description does not name a specific scanner or platform
Best for: Web developers and application security engineers who need practical vulnerability testing linked to actionable fixes for modern sites.
Not ideal for: Absolute beginners who need a gentle introduction, or buyers seeking confirmed instructions for a specific commercial scanner.
- Product type:Book
- Subject:Web application security
- Primary audience:Developers
- Coverage:Identifying and understanding vulnerabilities
- Testing content:Practical testing techniques
- Examples:Real-world exploit scenarios
- Remediation:Step-by-step strategies
- Technology focus:Modern web applications
Our verdict“Choose this if you already have some security foundation and want testing guidance tied directly to fixing vulnerabilities in modern applications.”
Grokking Web Application Security
Grokking Web Application Security is a broad subject-focused option, but the supplied information does not establish its tools, teaching style, or level of detail. That makes it harder to recommend as a direct web scanner how-to than Ultimate Pentesting for Web Applications, which names several testing tools, or Web Application Security: Finding and Fixing Exploits in Modern Websites, which describes testing and remediation steps. Its title may appeal to readers looking for a general grounding in application security rather than a guide centered on one scanner. The main tradeoff is limited evidence for choosing it: no specific exercises, vulnerability topics, or audience level are provided, so buyers who need practical scanner workflows should favor a title with more explicit coverage.
Pros:- Focuses on web application security as a broad subject
- Offers a general alternative to the named-tool emphasis of the Burp Suite and ZAP Proxy title
- May suit readers who want a wider security foundation rather than a single testing workflow
Cons:- Available product information does not specify tools, topics, or exercises
- The intended reader level and practical scanner coverage are not confirmed
Best for: Readers seeking a general web application security book and willing to verify its contents before relying on it for scanner training.
Not ideal for: Security practitioners who need confirmed scanner instructions, hands-on labs, or a stated remediation framework.
- Product type:Book
- Subject:Web application security
- Named scanners:Not specified
- Programming languages:Not specified
- Exercises:Not specified
- Format:Not specified
Our verdict“Consider this for broad security study, but choose a more explicitly tool- or remediation-focused book if your priority is scanner practice.”
How We Picked
I ranked these entries by how well their stated subject and approach match a buyer’s likely learning goal: building fundamentals, practicing web application testing, working with security tools, or exploring automation. I also weighed accessibility, practical orientation, subject breadth, and how much prior knowledge a reader may need. Because every listed item is a book, I did not treat any as a functioning scanner or compare software performance, integrations, or scan coverage.
The ordering favors a useful starting point for the broadest group, followed by more focused practical and advanced learning options. Titles centered on a narrow topic, or whose scope is difficult to distinguish from another entry, rank lower for general buyers. Before choosing, verify the edition, publication details, and table of contents; titles alone cannot confirm current tool support or depth.
| web application security scanner | Product type | Subject | Coverage |
|---|---|---|---|
| Beginner’s Guide to Web Applic | Introductory guide | Web application penetration testing | Fundamentals, essential concepts, and tools |
| Web Application Security: Expl | Book | Web application security | Exploitation and countermeasures |
| The Web Application Hacker’s H | Book | Web application security testing | Discovering and exploiting security flaws |
| Hands-on Penetration Testing f | Book | Web application penetration testing | Vulnerability assessment and exploitation |
| The Web Application Hacker’s H | Book | Web application security | Finding and exploiting security flaws |
| Automated Penetration Testing: | Book | Automated penetration testing | — |
| Web Application Security 101: | Book | Web application security | — |
| Ultimate Pentesting for Web Ap | Book | Web application penetration testing | — |
| Web Application Security: Find | Book | Web application security | Identifying and understanding vulnerabilities |
| Grokking Web Application Secur | Book | Web application security | — |
Factors to Consider When Choosing Web Application Security Scanners
These listings teach web application security; they do not scan your site. I’d choose a learning resource based on the skill you want to build, then select scanning software separately if you need results from an application.
Separate Learning Material From Scanning Software
A book can explain vulnerabilities, testing methods, and ways to interpret scanner findings, but it cannot crawl an application or generate a live report. If your immediate need is to check a website, look for a scanner that supports your application type and deployment process. If your goal is to learn how scanning fits into security work, a book may be a better first purchase. A common mistake is choosing a title from a scanner search and expecting it to include a usable software tool. Treat the two needs as separate: choose learning material for skills, and software for active testing.
Match the Book to Your Starting Point
Readers new to web security benefit from a gradual explanation of web behavior, vulnerabilities, and testing basics. A tool-heavy title may feel productive at first, but unfamiliar concepts can make its instructions difficult to apply. More experienced readers may prefer direct coverage of penetration testing or advanced workflows rather than introductory explanations. Check the contents for prerequisite knowledge, exercises, and the balance between concepts and procedures. Choose the level that challenges you without making every chapter depend on skills you have not yet learned.
Choose Between Broad Concepts and Tool Workflows
Broad security texts can help readers recognize vulnerabilities across different applications, while tool-oriented books may offer a more direct route to practicing a particular workflow. That practical focus can be useful, but tools and interfaces change, so instructions tied closely to specific versions may age faster than underlying security concepts. Before buying, check whether the book teaches transferable testing principles alongside named tools. A common misstep is equating a long list of tools in a title with deep coverage of each one. Prioritize the kind of knowledge you expect to use, not the number of tool names on the cover.
Check Edition, Currency, and Duplicate Listings
Security guidance can date as web frameworks, browser behavior, and testing tools evolve. Compare publication and edition details with the techniques you need, especially for books focused on named software. This roundup includes two listings for The Web Application Hacker’s Handbook with different subtitles, so verify whether they refer to distinct editions or overlapping material. Do not assume a newer-looking subtitle means a revised book or different content. When the listing provides limited detail, use the table of contents and publisher information to confirm what you are getting.
Decide Whether You Need Practical Exercises
Reading about an attack is different from learning to identify and validate it in a controlled environment. Readers aiming for hands-on skill should check for labs, exercises, sample applications, or step-by-step testing tasks. A conceptual guide may still be valuable for understanding why a finding matters, but it may not provide enough practice on its own. Do not experiment on systems without explicit authorization; use legal practice environments when a book calls for testing. Pairing theory with safe exercises often teaches more than collecting several books that cover the same concepts.
Know When to Pay More for Depth
A more specialized or advanced book can be worthwhile when it maps directly to a skill you need, such as hands-on penetration testing or automated agent design. Extra detail is less useful if you are still learning basic web security or need a working scanner today. Compare the contents, edition, and learning materials rather than judging value by page count or ambitious wording. For a beginner, one well-matched introduction plus practice may serve better than several overlapping references. For a working practitioner, a focused advanced resource can fill a specific knowledge gap.
Frequently Asked Questions
Are any of these entries web application security scanner software?
No. All ten entries are books about web application security, penetration testing, or related techniques. They may help you understand scanner output or learn how security testing works, but they do not scan a website themselves. If you need software, compare scanner platforms separately for application coverage, authentication handling, integrations, reporting, and deployment needs. Keep the book and software decisions distinct so you do not buy a learning resource expecting an operational tool.
Which title is the best starting point if I have no security background?
Grokking Web Application Security is the strongest starting point in this group based on its accessible framing, with Beginner’s Guide to Web Application Penetration Testing also aimed at entry-level learning. Check their contents for explanations of basic web concepts and guided practice before choosing. A beginner may find a specialized AI or advanced tool title harder to apply without those foundations. Plan to pair reading with safe, authorized exercises rather than treating a book as a substitute for practice.
Which book should I choose if I want hands-on testing practice?
Hands-on Penetration Testing for Web Applications is the most directly aligned title in this lineup for readers seeking applied testing workflows. The Burp Suite and proxy-focused title may suit readers who specifically want tool-centered learning, while a broad guide may spend more time on concepts. Check the table of contents for labs, examples, and the exact tools or versions covered; the title alone cannot confirm how much practice is included. Use only authorized targets or dedicated training environments for any testing exercises.
Are the two Web Application Hacker’s Handbook listings different books?
The list gives two different subtitles: one says Discovering and Exploiting Security Flaws and the other says Finding and Exploiting Security Flaws. That wording alone does not establish whether they are separate works, editions, or duplicate listings. Compare the author, publisher, edition, publication date, and contents before ordering. If the details match, buying both may add little; if they differ, the edition information should clarify which coverage you need.
Can a book here replace a scanner for a small business website?
No. A book can build the knowledge to plan tests and interpret findings, but it does not inspect your business website or produce a current vulnerability report. For active scanning, select software suited to your site’s technology, login requirements, and tolerance for test traffic, and run it only with proper authorization. A scanner can also miss issues or report findings that need human validation. A sensible approach is to use suitable software for detection and learning resources to improve how you review and respond to results.
Conclusion
For an all-around learning starting point, I’d choose Grokking Web Application Security; it is the best overall fit for readers who want an approachable foundation. The best value depends on your goal: if you are new, start with one beginner-oriented title rather than buying overlapping references. For a premium-level learning need, choose an advanced resource such as Automated Penetration Testing only if AI-driven security work matches your experience and interests. Beginners should favor clear fundamentals, while readers seeking practical testing should compare Hands-on Penetration Testing for Web Applications with the Burp Suite and proxy-focused guide. For scanner software specifically, none of these books is the right purchase on its own; choose a separate tool and use a book to strengthen your testing judgment.
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.