The best reverse engineering tools roundup is led by Practical Reverse Engineering, a strong all-around learning resource for readers who need coverage across architectures, operating systems, and analysis methods. For hands-on malware work, Practical Malware Analysis stands out; for a focused, approachable start, Reverse Engineering 101 is the simpler entry point. The main tradeoff is breadth versus specialization: broad guides build transferable foundations, while tool- or platform-specific books offer more depth in a narrower workflow. These products are books and learning resources rather than standalone software, so choose based on the tools and systems you need to analyze. Continue reading for the full comparison and recommendations by experience level and use case.

Get business pricing on monitors, keyboards and dev gear
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
Key Takeaways
- Practical Reverse Engineering earns the overall lead because its x86, x64, ARM, Windows kernel, tool, and obfuscation coverage serves more analysis paths than a single-platform guide.
- Practical Malware Analysis is the clearest specialist choice for malware investigation, while its security-focused scope makes it less suited to readers mainly studying firmware or general program behavior.
- Ghidra Essentials and The radare2 Black Book focus on different tool workflows; pick based on the environment you plan to use rather than expecting one guide to teach both.
- The firmware-focused handbook and the UEFI, embedded, IoT, and BMC guide address a distinct hardware-facing skill set that general software reversing books cannot replace.
- The beginner titles provide gentler entry points, while scripting and automation books make more sense after readers understand disassembly, debugging, and analysis basics.





| reverse engineering tool | Format | Topics |
|---|---|---|
| Embedded Systems Reverse Engin | Book | — |
| Practical Reverse Engineering: | Book | — |
| Practical Malware Analysis: Th | Book | — |
| x86 Software Reverse Engineeri | Book | — |
| Advanced Reverse Engineering a | Book | — |
| Reverse Engineering 101: A Beg | Not specified | — |
| The Complete Reverse Engineer | Book | Assembly basics, reverse engineering, threat analysis |
| Foundations of Linux Debugging | Not specified | Binary analysis, stack memory, C/C++ code reconstruction |
| Sockets | Not specified | Shellcode, exploit reverse engineering, exploit porting |
| Blue Fox: Arm Assembly Interna | Not specified | Assembly internals, reverse engineering |
| Firmware and Hardware Reverse | Book | UEFI, embedded devices, IoT, BMC, trusted execution environments |
| The radare2 Black Book: Advanc | Book | Advanced binary analysis, malware reverse engineering, debugging |
| Ghidra Essentials: Mastering S | Book | Software reverse engineering and malware analysis |
| Advanced Ghidra Scripting Cook | Book | Ghidra scripting, reverse engineering, malware analysis |
More Details on Our Top Picks
Embedded Systems Reverse Engineering Handbook
Embedded-focused coverage sets this book apart from Practical Reverse Engineering, whose title points to software, processor architectures, and kernel analysis. Here, the emphasis is on firmware, ROM extraction, hardware debugging, and IoT security, with UART, JTAG, SPI, and I2C techniques tied to practical embedded work. That focus can help engineers connect signals and interfaces on a device to the firmware they are trying to understand. The tradeoff is specialization: readers seeking a broad software-reversing foundation or a general electronics reference may find the scope narrow. Its stated technical depth also makes it a tougher starting point than an introductory guide such as Reverse Engineering 101. I’d choose it when physical devices and firmware are the target, not as a catch-all reversing reference.
Pros:- Covers firmware analysis and ROM extraction alongside hardware debugging
- Includes techniques involving UART, JTAG, SPI, and I2C
- Connects embedded reverse engineering with IoT security challenges
Cons:- Technical material may challenge readers without embedded-systems experience
- Its narrow focus offers limited value as a general electronics or software-reversing reference
Best for: Engineers and security researchers investigating embedded devices, IoT products, or firmware through hardware interfaces
Not ideal for: Newcomers seeking a gentle introduction to software reversing, or readers who need a broad electronics textbook
- Format:Book
- Primary focus:Embedded systems reverse engineering
- Firmware topics:Firmware analysis and ROM extraction
- Hardware topics:Hardware debugging
- Interfaces covered:UART, JTAG, SPI, and I2C
- Security focus:IoT security
Our verdict“Choose this for hands-on embedded and IoT investigations; pick Practical Reverse Engineering for a broader software and architecture focus.”
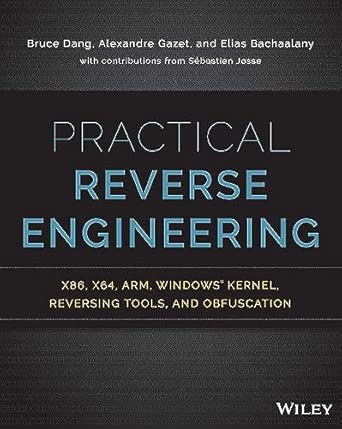
Practical Reverse Engineering: x86, x64, ARM, Windows Kernel, Reversing Tools, and Obfuscation
Architecture breadth is the clearest reason to choose this title: its scope names x86, x64, ARM, and the Windows kernel, along with reversing tools and obfuscation. That makes it a stronger match for software analysts who need to move between processor families than x86 Software Reverse Engineering, Cracking, and Countermeasures, which is explicitly centered on x86. The tradeoff is that this is not the embedded hardware guide in the lineup; Embedded Systems Reverse Engineering Handbook is the more direct fit for ROM extraction and UART or JTAG work. The supplied product information gives a subject list but no detail on exercises, tools, or depth, so I would select it for its stated range rather than assume a particular learning format. It suits readers with some technical grounding better than a first introduction.
Pros:- Names x86, x64, and ARM in its stated scope
- Includes Windows kernel reverse engineering
- Covers reversing tools and obfuscation as well as processor architectures
Cons:- Available product details do not establish the book’s depth, exercise format, or specific tools
- The stated software focus is less suited to hardware and embedded-interface investigations
Best for: Software security analysts and developers who need a reference spanning x86, x64, ARM, Windows kernel topics, and obfuscation
Not ideal for: Readers focused on hardware interfaces or embedded firmware, or beginners who need confirmed step-by-step exercises
- Format:Book
- Architectures:x86, x64, and ARM
- Kernel topic:Windows kernel
- Additional topics:Reversing tools and obfuscation
- Primary focus:Practical software reverse engineering
- ASIN:1118787315
Our verdict“Pick this when you want a software-reversing reference spanning several architectures; choose the Embedded Systems Reverse Engineering Handbook for device-level work.”
Practical Malware Analysis: The Hands-On Guide to Dissecting Malicious Software
Malware is the organizing lens here, making this a more targeted choice than Advanced Reverse Engineering and Binary Analysis, whose stated subject range also includes firmware, control flow, and general executable analysis. The title promises a hands-on guide to dissecting malicious software, so it is most relevant to readers who want reverse engineering in service of understanding malware rather than hardware devices or broad architectural study. The available description is brief, however; it does not specify platforms, tools, lab setup, or the exact exercises. That limits how confidently I can match it to a particular workflow. Compared with Embedded Systems Reverse Engineering Handbook, it is the clearer fit for malicious software and the weaker fit for firmware interfaces. I’d choose it for a malware-focused reading path, not as a general reverse-engineering survey.
Pros:- Centers its subject matter on malicious software analysis
- Describes a hands-on approach to dissecting malware
- Offers a more focused malware path than broad binary-analysis titles
Cons:- Available description does not identify tools, platforms, or lab requirements
- Its malware emphasis may not serve readers seeking firmware or general architecture coverage
Best for: Security analysts and students whose primary goal is to dissect and understand malicious software
Not ideal for: Embedded engineers, hardware researchers, or buyers needing confirmed coverage of particular operating systems and analysis tools
- Format:Book
- Primary focus:Malware analysis
- Approach:Hands-on guide
- Subject:Dissecting malicious software
- ASIN:1593272901
- Subtitle:The Hands-On Guide to Dissecting Malicious Software
Our verdict“Choose this for a malware-centered learning path, while readers seeking wider executable and firmware topics should compare it with Advanced Reverse Engineering and Binary Analysis.”
x86 Software Reverse Engineering, Cracking, and Countermeasures (Tech Today)
x86 specialization gives this book a distinct place in the lineup: it pairs software reverse engineering with cracking and countermeasures, rather than aiming for the architecture range named by Practical Reverse Engineering. That pairing may appeal to readers studying how software protections are examined and defended. It is also a narrower choice: the supplied details identify x86, but do not confirm coverage of other architectures, particular tools, or a practical exercise structure. For broader binary topics such as firmware, decompilers, and memory, Advanced Reverse Engineering and Binary Analysis has a wider stated scope. I would treat this as a focused title for x86 software analysis and protection topics, not a first-stop reference for every reverse-engineering task. The product information is limited, so buyers should not infer specifics beyond its title and listed subjects.
Pros:- Directly addresses x86 software reverse engineering
- Pairs cracking topics with countermeasures
- Has a more specific x86 focus than cross-architecture references
Cons:- Provided details do not establish coverage beyond x86
- No description is available to confirm tools, depth, or practical exercises
Best for: Readers studying x86 software analysis, software cracking concepts, and countermeasures
Not ideal for: Researchers focused on ARM, embedded hardware, or buyers who need a clearly documented toolset and exercise plan
- Format:Book
- Series:Tech Today
- Architecture focus:x86
- Primary topics:Software reverse engineering and cracking
- Related topic:Countermeasures
- ASIN:1394199880
Our verdict“Choose this for a focused look at x86 reversing and countermeasures; readers needing broader architecture coverage should favor Practical Reverse Engineering.”
Advanced Reverse Engineering and Binary Analysis: Understanding Executables, Assembly Language, Decompilers, Debuggers, Memory, Control Flow, Firmware, and Malware
Wide subject coverage is this book’s main advantage: its description spans executables, assembly, decompilers, debuggers, memory, control flow, firmware, and malware. That makes it a more general binary-analysis pick than Practical Malware Analysis, which centers on malicious software, and a broader software-and-firmware survey than the hardware-interface focus of Embedded Systems Reverse Engineering Handbook. The breadth may help readers connect low-level concepts across different targets, but the description does not name processor architectures, tools, or a teaching sequence. Buyers who need a narrowly defined path—such as x86 cracking or embedded UART and JTAG work—may be better served by a specialized title. I’d shortlist it when topic range matters more than confirmed platform-specific instruction, while treating its practical depth as unclear from the supplied information.
Pros:- Covers executables, assembly language, decompilers, and debuggers
- Includes memory and control-flow analysis topics
- Connects software binary analysis with firmware and malware
Cons:- Available details do not identify specific architectures or tools
- Broad scope may be less direct than a malware- or hardware-focused guide
Best for: Intermediate readers seeking a broad reference across executable analysis, debugging, firmware, and malware topics
Not ideal for: Beginners who need a clearly described progression, or specialists seeking confirmed coverage of a particular architecture or tool
- Format:Book
- Primary focus:Reverse engineering and binary analysis
- Executable topics:Executables, assembly language, and control flow
- Analysis tools covered:Decompilers and debuggers
- Additional technical topics:Memory analysis
- Target areas:Firmware and malware
Our verdict“Choose this for a wide-ranging binary-analysis topic map; select Practical Malware Analysis or the Embedded Systems Reverse Engineering Handbook for a more focused path.”
Reverse Engineering 101: A Beginner’s Guide to Software Deconstruction
Reverse Engineering 101 is the most approachable-sounding entry in this group for readers starting with software deconstruction. Its beginner focus sets it apart from The Complete Reverse Engineer 101, whose stated scope reaches from assembly fundamentals to advanced threat analysis. The supplied information for this title is sparse, though, so I can’t verify which tools, platforms, or hands-on exercises it covers. That makes it a possible starting point for learning concepts, not a clearly documented practical reference. Compared with Foundations of Linux Debugging, Disassembling, and Reversing, it also has no specified Linux or Intel x64 focus to guide buyers seeking platform-specific instruction. Choose it only if an introductory framing matters more than confirmed technical coverage.
Pros:- Explicitly aimed at beginners
- Focuses on software deconstruction and reverse engineering
- May suit readers who want an introductory framing before specialized study
Cons:- The supplied product information does not identify tools, platforms, or specific techniques
- No details establish how much practical work or technical depth the guide provides
Best for: Readers new to software reverse engineering who want a beginner-oriented introduction and are comfortable checking the book’s contents before relying on it.
Not ideal for: Linux or Intel x64 practitioners seeking confirmed coverage of debugging, binary analysis, or C/C++ reconstruction.
- Format:Not specified
- Audience:Beginners
- Subject:Software reverse engineering
- Focus:Software deconstruction
- Platform:Not specified
- Architecture:Not specified
Our verdict“A tentative starting point for newcomers, but buyers needing verified topics or hands-on coverage should choose a more specifically documented guide.”
The Complete Reverse Engineer 101: From Assembly Basics to Advanced Threat Analysis (Reverse Engineering & Security Research, Book 2)
The Complete Reverse Engineer 101 stands out for its stated span: assembly fundamentals through advanced threat analysis. That range may appeal to readers who want reverse engineering linked to security research, rather than a narrower platform-specific route like Foundations of Linux Debugging, Disassembling, and Reversing, which specifies Linux and Intel x64. Its place as Book 2 in the Reverse Engineering & Security Research series is a useful clue that it may fit an ongoing study plan, but the supplied details don’t say what Book 1 covers or whether this volume works independently. The scope sounds ambitious; without chapter or exercise details, I can’t judge how deeply it treats each topic. Readers prioritizing confirmed Linux examples may prefer Foundations instead.
Pros:- Stated coverage spans assembly fundamentals and threat analysis
- Connects reverse engineering with security research
- Part of a specifically named series
Cons:- The supplied information does not explain chapter structure or practical exercises
- As Book 2, its dependence on earlier material is unclear
- No operating system or processor architecture is specified
Best for: Security learners who want a book described as connecting assembly basics with threat analysis and are interested in a reverse engineering series.
Not ideal for: Buyers who need a documented platform-specific lab guide, a confirmed standalone introduction, or detailed information about exercises and tools.
- Format:Book
- Series:Reverse Engineering & Security Research
- Series number:2
- Topics:Assembly basics, reverse engineering, threat analysis
- Platform:Not specified
- Architecture:Not specified
Our verdict“Choose it for the breadth of its stated security topics, but prefer a platform-specific guide if you need confirmed hands-on coverage.”
Foundations of Linux Debugging, Disassembling, and Reversing
Foundations of Linux Debugging, Disassembling, and Reversing is the clearest fit here for readers working on Linux binaries: its stated scope includes Intel x64, stack memory, binary analysis, and reconstructing C and C++ code. That specificity gives it a practical advantage over the broadly framed Reverse Engineering 101, whose supplied details don’t identify a platform or technical topics. It also offers a more focused alternative to The Complete Reverse Engineer 101, which describes a wider path into threat analysis but doesn’t specify an architecture. The tradeoff is specialization: this book’s documented emphasis won’t directly cover ARM assembly or exploit porting. I’d put it ahead for Linux-focused study, but not for readers seeking a cross-platform survey.
Pros:- Specifies Linux and Intel x64 as its technical focus
- Covers binary code analysis and disassembly
- Addresses stack memory usage
- Connects reverse engineering with C and C++ code reconstruction
Cons:- Its Linux and Intel x64 focus limits direct relevance to other platforms and architectures
- The supplied details do not identify tools, exercises, or the book’s level
Best for: Developers and security analysts studying Linux binaries on Intel x64 who want to connect stack behavior and disassembly with C/C++ reconstruction.
Not ideal for: Readers focused on ARM, embedded firmware, exploit porting, or a broad introduction that spans multiple platforms.
- Platform:Linux
- Architecture:Intel x64
- Topics:Binary analysis, stack memory, C/C++ code reconstruction
- Focus:Debugging, disassembling, and reverse engineering
- Programming languages:C and C++
- Format:Not specified
Our verdict“Pick this for Linux and Intel x64 binary work; choose a broader or ARM-focused title for other targets.”
Sockets, Shellcode, Porting, and Coding: Reverse Engineering Exploits and Tool Coding for Security Professionals
Sockets, Shellcode, Porting, and Coding is the most directly oriented toward exploit work in this set, pairing shellcode analysis with exploit porting and security tool development. That makes it a different choice from Foundations of Linux Debugging, Disassembling, and Reversing, which centers on binary analysis and C/C++ reconstruction on Linux and Intel x64. Here, the appeal is applying reverse engineering to understand and adapt exploitation techniques, not following a general beginner curriculum. The stated audience is intermediate to advanced, and the book assumes prior low-level programming and reverse engineering knowledge. That prerequisite is a meaningful barrier for newcomers, while the supplied details don’t name supported platforms or specific tools. Readers seeking a fundamentals-first route should start elsewhere.
Pros:- Combines reverse engineering concepts with coding examples
- Covers shellcode creation and analysis
- Addresses exploit porting across platforms
- Includes security tool development
Cons:- Assumes prior low-level programming and reverse engineering knowledge
- The supplied details do not identify supported platforms or architectures
- Its exploitation focus is narrower than a general binary-analysis reference
Best for: Intermediate or advanced security practitioners with low-level programming experience who want to study shellcode, exploit porting, and security tool coding.
Not ideal for: Beginners who need assembly or reverse engineering fundamentals, and readers who require confirmed platform-specific instructions.
- Audience:Intermediate to advanced security practitioners
- Topics:Shellcode, exploit reverse engineering, exploit porting
- Tool development:Security tool coding
- Approach:Theory and practical coding examples
- Prerequisites:Low-level programming and reverse engineering knowledge
- Format:Not specified
Our verdict“Choose this for exploit-focused reverse engineering and tool coding if you already have low-level experience.”
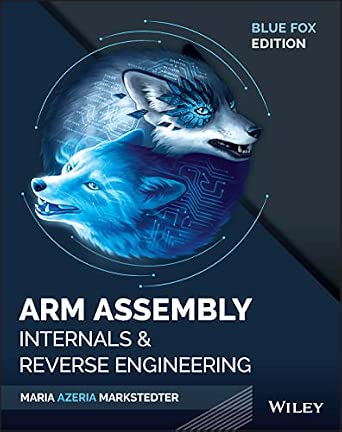
Blue Fox: Arm Assembly Internals and Reverse Engineering
Blue Fox: Arm Assembly Internals and Reverse Engineering is the only title in this batch whose name explicitly points to ARM assembly, giving it a distinct role for readers studying that architecture. It offers a clear contrast with Foundations of Linux Debugging, Disassembling, and Reversing, which specifies Linux and Intel x64 rather than ARM. That makes Blue Fox the more relevant title to investigate for ARM-focused reverse engineering, but the supplied product data contains no description, topic breakdown, or other technical details beyond the title. I can’t confirm its platform coverage, teaching level, tools, or practical exercises. Buyers should treat the architecture signal as a useful starting point, not proof of a complete ARM workflow. For documented Linux x64 topics, Foundations is the safer fit.
Pros:- Title explicitly identifies ARM assembly as its subject
- Pairs assembly internals with reverse engineering
- Provides an architecture-specific alternative to the Linux and Intel x64 focus of Foundations
Cons:- No product description or topic breakdown was supplied
- Tools, target platforms, and practical exercises are not specified
- Audience level and scope cannot be established from the provided data
Best for: Readers specifically seeking an ARM assembly and reverse engineering book who can confirm its level and coverage before purchase.
Not ideal for: Buyers who need verified tool instructions, detailed ARM platform coverage, or a clearly described beginner-to-advanced curriculum.
- Architecture:ARM
- Topics:Assembly internals, reverse engineering
- Platform:Not specified
- Tools:Not specified
- Audience level:Not specified
- Format:Not specified
Our verdict“Consider it for ARM-focused study only after checking its detailed contents, since the available information confirms little beyond the title.”
Firmware and Hardware Reverse Engineering: UEFI, Embedded Devices, IoT, BMC, and Trusted Execution Environments Using Python, C, and Ghidra
This book is the most hardware-focused choice in this group, connecting reverse engineering techniques to UEFI, embedded devices, IoT, BMC, and trusted execution environments. Its coverage of Python, C, and Ghidra gives readers several ways to approach analysis, rather than centering the work on one application. Compared with Ghidra Essentials, which focuses on software reverse engineering and malware analysis, this title points toward firmware and device-specific challenges. The breadth is its main advantage, but also its tradeoff: readers seeking a narrow, step-by-step guide to Ghidra scripting may get more focused help from Advanced Ghidra Scripting Cookbook. I’d choose this for security researchers working across device and firmware boundaries, not as a general first introduction to reverse engineering.
Pros:- Covers a broad range of firmware and hardware targets, including UEFI, IoT, and BMC
- Pairs Ghidra analysis with Python and C
- Focuses on device and firmware work rather than software binaries alone
Cons:- Its broad topic range may provide less depth on any one platform than a specialist guide
- The listed topics do not establish a beginner-friendly learning path
- Readers focused on Ghidra automation may prefer a scripting-specific book
Best for: Security researchers and embedded developers who need to study firmware across UEFI, IoT, BMC, and trusted execution environments.
Not ideal for: Readers seeking a beginner-focused introduction to software reverse engineering or a dedicated guide to automating Ghidra workflows.
- Format:Book
- Topics:UEFI, embedded devices, IoT, BMC, trusted execution environments
- Tools and languages:Python, C, Ghidra
- Focus:Firmware and hardware reverse engineering
- Device coverage:Embedded devices and IoT
- Firmware and platform coverage:UEFI, BMC, trusted execution environments
Our verdict“Choose this book if your reverse engineering work centers on firmware and connected devices rather than general software binaries.”
The radare2 Black Book: Advanced Binary Analysis, Malware Reverse Engineering, Debugging, and R2pipe Automation
The radare2 Black Book stands apart through its focus on a single analysis toolkit: radare2, with R2pipe automation as a related workflow. Its subject mix spans binary analysis, debugging, and malware reverse engineering, making it a stronger match for readers who want to work inside that tool ecosystem than for those looking for broad hardware coverage. Compared with Ghidra Essentials, this title puts radare2 at the center rather than Ghidra; that choice matters if a reader wants to build repeatable scripts around R2pipe. The tradeoff is specialization: the supplied details do not describe wider platform coverage or a beginner path. I’d pick it for analysts committed to radare2, while readers prioritizing Ghidra-based workflows should choose one of the Ghidra titles instead.
Pros:- Covers advanced binary analysis and debugging with radare2
- Includes malware reverse engineering
- Addresses R2pipe automation for repeatable analysis tasks
Cons:- Its radare2 focus is a limitation for readers standardizing on Ghidra
- The supplied description does not specify beginner guidance or prerequisite coverage
- Its listed scope does not highlight firmware or hardware analysis
Best for: Malware analysts and security researchers who want to use radare2 for binary analysis, debugging, and R2pipe automation.
Not ideal for: Readers who need a Ghidra-centered workflow, broad firmware coverage, or an explicitly beginner-oriented introduction.
- Format:Book
- Primary tool:radare2
- Automation tool:R2pipe
- Topics:Advanced binary analysis, malware reverse engineering, debugging
- Automation focus:R2pipe automation
- Intended work:Cybersecurity research and professional analysis
Our verdict“Choose this book if radare2 and R2pipe are central to your binary analysis work; choose a Ghidra title if they are not.”
Ghidra Essentials: Mastering Software Reverse Engineering and Malware Analysis
Ghidra Essentials is the direct pick for readers who want a book centered on one widely used reverse engineering tool. Its stated focus combines software reverse engineering and malware analysis, giving it a clearer software-analysis lane than the firmware-focused Firmware and Hardware Reverse Engineering. It also differs from Advanced Ghidra Scripting Cookbook: this title presents broader Ghidra-based analysis, while the cookbook is specifically oriented around Python automation, headless processing, and triage. The tradeoff is that the available information does not identify particular Ghidra features, scripting coverage, or a prerequisite level, so buyers seeking those specifics may prefer the more narrowly defined cookbook. I’d favor this book for readers who want a Ghidra-focused software analysis guide, not those whose work is mainly hardware or firmware.
Pros:- Centers on Ghidra for software reverse engineering
- Includes malware analysis alongside general software analysis
- Identified as part of The Modern Linux Developer Series
Cons:- The supplied description does not specify scripting or automation coverage
- No particular processor architectures or binary formats are identified
- The listed scope is less suited to hardware and firmware research than the firmware-focused title
Best for: Software security learners and malware analysts seeking a Ghidra-centered book on reverse engineering and analysis.
Not ideal for: Firmware specialists or analysts looking primarily for Python scripting recipes, headless workflows, and rapid binary triage.
- Format:Book
- Primary tool:Ghidra
- Topics:Software reverse engineering and malware analysis
- Series:The Modern Linux Developer Series
- Book number:4
- Analysis focus:Software
Our verdict“Choose this for Ghidra-based software and malware analysis; opt for the cookbook if automation is your main need.”
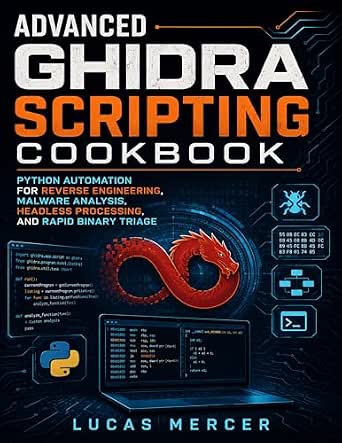
Advanced Ghidra Scripting Cookbook: Python Automation for Reverse Engineering, Malware Analysis, Headless Processing, and Rapid Binary Triage
This cookbook is the most workflow-specific option here: it focuses on automating Ghidra tasks with Python, including headless processing and rapid binary triage. That makes it a better fit for analysts handling repeated or batch-oriented work than Ghidra Essentials, whose listed scope is broader software reverse engineering and malware analysis. It also offers a different path from The radare2 Black Book, which addresses automation through R2pipe rather than Ghidra scripting. The clear tradeoff is its narrow tool focus: readers who need a general introduction, non-Ghidra methods, or firmware topics may find the other books more relevant. The supplied description gives useful topic coverage but no detail on individual recipes or assumed Python skill, so I’d choose it when the automation use case is already clear.
Pros:- Targets practical Ghidra scripting and Python automation
- Covers headless processing and rapid binary triage
- Connects automation workflows to reverse engineering and malware analysis
- Identifies a specific use case for reducing repetitive analysis tasks
Cons:- Its Ghidra-specific scope is less useful to analysts working mainly in radare2
- The supplied information does not state required Python or Ghidra experience
- No individual recipe examples or supported platforms are specified
Best for: Reverse engineers and malware analysts who already use Ghidra and want Python-driven automation for headless analysis or binary triage.
Not ideal for: Beginners seeking a broad introduction to reverse engineering, or analysts whose primary tool is radare2 or whose focus is device firmware.
- Format:Book
- Primary tool:Ghidra
- Automation language:Python
- Topics:Ghidra scripting, reverse engineering, malware analysis
- Processing workflow:Headless processing
- Triage workflow:Rapid binary triage
- Series:Modern Developer Toolkit
- Series volume:4
Our verdict“Choose this cookbook if you already work in Ghidra and want automation recipes more than a general reverse engineering introduction.”

How We Picked
I compared these 14 books as reverse-engineering learning resources, not as standalone software products. The ranking favors coverage that helps readers build transferable skills: interpreting binaries, working with disassemblers and debuggers, understanding architectures, and connecting analysis to a practical goal such as malware research or firmware inspection. I also weighed how clearly each title signals its intended reader and whether its focus fills a real gap in the lineup.
Practical Reverse Engineering ranks first for its range across architectures and analysis topics. Specialist books rank higher for the audience they serve, not because they replace a broad foundation: malware, Ghidra, radare2, Linux debugging, ARM, and firmware each have distinct roles. Beginner guides favor accessibility, while scripting and exploit-development titles are better suited to readers with existing technical grounding. Since these are books, buyers should check edition, examples, and software-version compatibility before choosing.
| reverse engineering tool | Format |
|---|---|
| Embedded Systems Reverse Engin | Book |
| Practical Reverse Engineering: | Book |
| Practical Malware Analysis: Th | Book |
| x86 Software Reverse Engineeri | Book |
| Advanced Reverse Engineering a | Book |
| Reverse Engineering 101: A Beg | Not specified |
| The Complete Reverse Engineer | Book |
| Foundations of Linux Debugging | Not specified |
| Sockets | Not specified |
| Blue Fox: Arm Assembly Interna | Not specified |
| Firmware and Hardware Reverse | Book |
| The radare2 Black Book: Advanc | Book |
| Ghidra Essentials: Mastering S | Book |
| Advanced Ghidra Scripting Cook | Book |
Factors to Consider When Choosing Best Reverse Engineering Tools
Choosing among these titles starts with the work you want to do, not the tool name on the cover. Use these factors to avoid buying a narrow specialist guide when you need foundations—or a broad introduction when you already need a specific workflow.
Match the resource to your analysis target
Software binaries, malware samples, and embedded firmware share techniques, but they create different practical problems. A general reversing text can explain assembly and control flow without showing how to handle device images or hardware-specific constraints. Before choosing, name the target you expect to analyze most often: desktop software, Linux binaries, malicious code, or firmware. A common mistake is choosing a book for its broad-sounding title without checking whether its examples match that target. If your work may span several areas, start with transferable foundations and add a specialist resource later. This approach reduces the chance of learning a workflow that does not fit your actual tasks.
Choose breadth or tool-specific depth
A tool-focused guide can help you move faster in one environment, but it may not teach concepts that transfer cleanly to another. Broader books tend to build a mental model of binaries, architectures, and analysis techniques, even if they spend less time on a particular interface. Decide whether your immediate need is understanding reverse engineering or becoming productive in a specific tool. Avoid treating a tool manual as a substitute for learning assembly and program behavior. Readers who already know the fundamentals may get more value from a focused Ghidra or radare2 resource. Beginners usually benefit from concepts first, then tool-specific practice.
Check architecture and operating-system coverage
Architecture affects instruction sets, calling conventions, and the way you interpret code; operating systems add their own formats and debugging concerns. A book centered on x86 may not prepare you for ARM-based devices, and a Windows-focused guide will not automatically address Linux workflows. Compare the examples with the binaries you expect to encounter rather than assuming skills transfer without adjustment. If you have no fixed target, a resource covering multiple architectures can help you recognize what changes between platforms. If your role is already specialized, concentrated coverage may be more useful than a broad survey. Confirm that the edition’s examples and tools remain compatible with your intended setup.
Be realistic about your starting knowledge
Reverse engineering draws on programming, operating-system concepts, and low-level computer architecture, so a book pitched at beginners may still assume some technical comfort. Look for signs of the intended level, such as whether the material begins with assembly basics or moves quickly into kernel analysis, scripting, or threat research. Buying an advanced guide too early can leave you copying commands without understanding the evidence they produce. On the other hand, an introductory resource may repeat material you already know. Match the book to the skill you need to build next, not to the most advanced topic in its title. A short foundation-building step can make later specialist material far more useful.
Treat scripting and automation as a second stage
Automation can speed up triage and repeated analysis, but scripts are only reliable when you understand what they are measuring. A scripting cookbook is most useful after you can interpret disassembly, identify relevant program behavior, and check whether automated output makes sense. Newcomers sometimes reach for automation to avoid learning the underlying workflow, which can hide errors rather than remove them. Consider whether your work involves enough repeated binaries to justify investing in scripting techniques. For occasional manual analysis, a fundamentals guide may offer more immediate value. For recurring workloads, automation-focused material can help turn a one-off process into a repeatable method.
Check safety, legality, and lab requirements
Some topics in this lineup involve malware, exploit development, or device firmware, which call for a controlled lab and clear authorization. A book can explain analysis methods, but it cannot make an unsafe setup safe or grant permission to examine a system. Before studying operational examples, plan for isolated virtual machines, disposable snapshots, and network controls appropriate to your work. Check whether the material depends on software, hardware, or sample files you can access. Readers should also distinguish defensive analysis from actions against systems they do not own or have permission to test. These practical constraints can determine which resource is useful right now, even when its subject matches your interests.
Frequently Asked Questions
Are these reverse engineering tools software or books?
This roundup compares books and learning resources, not downloadable disassemblers or debuggers. Titles such as Ghidra Essentials and The radare2 Black Book teach workflows around named tools, while other books focus on broader analysis skills. If you need software to analyze a binary, you will need to obtain and install the relevant tool separately. Check each book’s edition and examples to see whether its instructions fit the software version you plan to use. A tool guide is most useful when paired with access to that tool and suitable practice files.
Which book should I start with if I have never analyzed a binary?
Start with Reverse Engineering 101 if you want an explicitly beginner-oriented introduction, or choose Practical Reverse Engineering if you already have programming and low-level computing experience and want broader coverage. The right choice depends on how comfortable you are with assembly, operating systems, and debugging concepts. A beginner title may make the first steps less abrupt, while the broader book can reduce the need to switch resources as your interests expand. Avoid starting with scripting, kernel, or exploit-development material unless you already have the foundations those topics rely on. Use the first chapters or sample material, when available, to check the assumed background.
Should I choose a Ghidra guide or a radare2 guide?
Choose based on the tool you expect to use and the workflow you need to learn; the two guides are not interchangeable introductions to every reversing task. Ghidra Essentials is the direct fit for readers building a Ghidra workflow, while The radare2 Black Book targets readers interested in radare2, advanced binary analysis, and automation through R2pipe. If you have not committed to either, first learn core concepts such as control flow and assembly so tool differences are easier to judge. Check current tool versions and examples, since interfaces and commands can change. You can add a second guide later if your work calls for both environments.
Do I need a specialist firmware book if I already know software reversing?
Software reversing knowledge provides a helpful base, but firmware work can involve device images, boot processes, hardware interfaces, and platform-specific constraints that general binary analysis books may not cover. A firmware-focused title makes sense if your target includes embedded devices, UEFI, IoT, BMCs, or trusted execution environments. If your work is limited to desktop applications or malware samples, that specialized coverage may not serve your immediate needs. Consider whether you can access compatible hardware or sample firmware for practice, since reading alone may not reproduce the full workflow. A broad foundation plus a firmware guide is often a better fit than expecting either one to cover everything.
When should I buy an automation or exploit-development book?
Choose an automation title when you already understand the analysis steps you want to repeat and need to make them faster or more consistent. Choose exploit-development material when your work specifically requires understanding exploit construction, shellcode, or related tooling and you have the relevant programming background. Neither is the easiest route for learning basic disassembly from scratch. Before committing, check the assumed skill level, examples, and dependencies, including whether the exercises require particular operating systems or tools. If you are still learning to interpret code manually, a fundamentals or tool-workflow book is likely a more productive first step.
Conclusion
Best overall: choose Practical Reverse Engineering for its broad architecture and analysis coverage. Best value for focused malware study: Practical Malware Analysis is the direct specialist pick; for a broad first foundation, Reverse Engineering 101 is the more approachable starting point. Best premium-level depth: Advanced Reverse Engineering and Binary Analysis suits readers ready for more demanding coverage, while its scope may be excessive for beginners. For specific needs, choose Ghidra Essentials or The radare2 Black Book by your preferred tool, and pick the firmware or ARM titles when those targets match your work. My simplest recommendation is to begin with the broad or beginner resource that fits your current knowledge, then add a specialist guide once your analysis target is clear.
Halloween Picks
halloween
As an affiliate, we earn on qualifying purchases.